Compliance Vault
The Regulatory Mediator between RBI and DPDP Act 2023.
RBI mandates 5-year KYC retention. The DPDP Act requires erasure on demand. Two Indian laws. Two conflicting obligations. From 13 May 2027, when DPDP obligations and penalties commence, both apply to the same record.
The Compliance Vault carries the Legal Obligation Override. Retention mandates sit in a conflict register, matching erasure requests are flagged, and each flag leaves a signed denial register entry naming the statute and the retention period.
Every flagged erasure request leaves a signed entry citing the law and the retention period behind it.
Regulatory Signal: RBI Business Conduct Directions
The RBI Responsible Business Conduct Second Amendment Directions, 2026, notified on 15 June 2026 for commercial banks and NBFCs, require explicit consent for each product or service and ban compulsory bundling and dark patterns. They come into effect on 1 January 2027.
Regulatory Watch: May 19, 2026
On May 19, 2026, the Supreme Court directed the Ministry of Electronics and IT to examine a petition seeking the recovery of stolen personal data held on foreign servers. Cross-border data handling is drawing judicial attention.
The Conflict
Two regulators. Two conflicting mandates.
The table below maps each data category to its RBI requirement, the conflicting DPDP obligation, and how the Compliance Vault supports resolving both simultaneously.
How It Works
The Legal Obligation Override: three steps.
Each stage leaves a record in the app. The policy document records intent; these records show what was done with each request.
01
Register
Your team records each retention mandate in the conflict register: the regulation and its section, the DPDP provision it engages, the statutory instrument and the retention period. The RBI KYC Directions 2025 entry is seeded; your team adds others, such as the PMLA rules, as its own entries.
02
Flag
When a Data Principal files an erasure request through your public rights portal, ConsentOS matches it against the register entries for your sector. A match flags the request before anyone acts on it.
03
Document
Each match writes a signed entry to the denial register: the request reference, the register entry matched, the statutory instrument and the retention period, with an HMAC-SHA256 signature over those fields and the signing time. Your compliance lead reviews the flag and records the decision.
Walkthrough
An NBFC receives a DPDP erasure request. Here is what happens.
Four stages, from the request arriving to a signed entry your team can produce on demand.
01
The Request
A Data Principal files an erasure request through the NBFC's rights portal, covering name, address, loan history and KYC documents.
02
The Check
ConsentOS matches the request against the conflict register entries for the NBFC's sector. The KYC entry, citing the RBI KYC Directions 2025, Chapter VII (Record Management), matches, and the request is flagged.
03
The Override
A signed entry is written to the denial register with the statutory instrument, the retention period, the matched register entry and the signing time. The compliance team reviews the flag and records its decision on the request.
04
The Evidence
The denial register accepts new entries only. A database trigger rejects edits and deletions. If the Data Protection Board inquires into a refusal, the entry names the statute and the period.
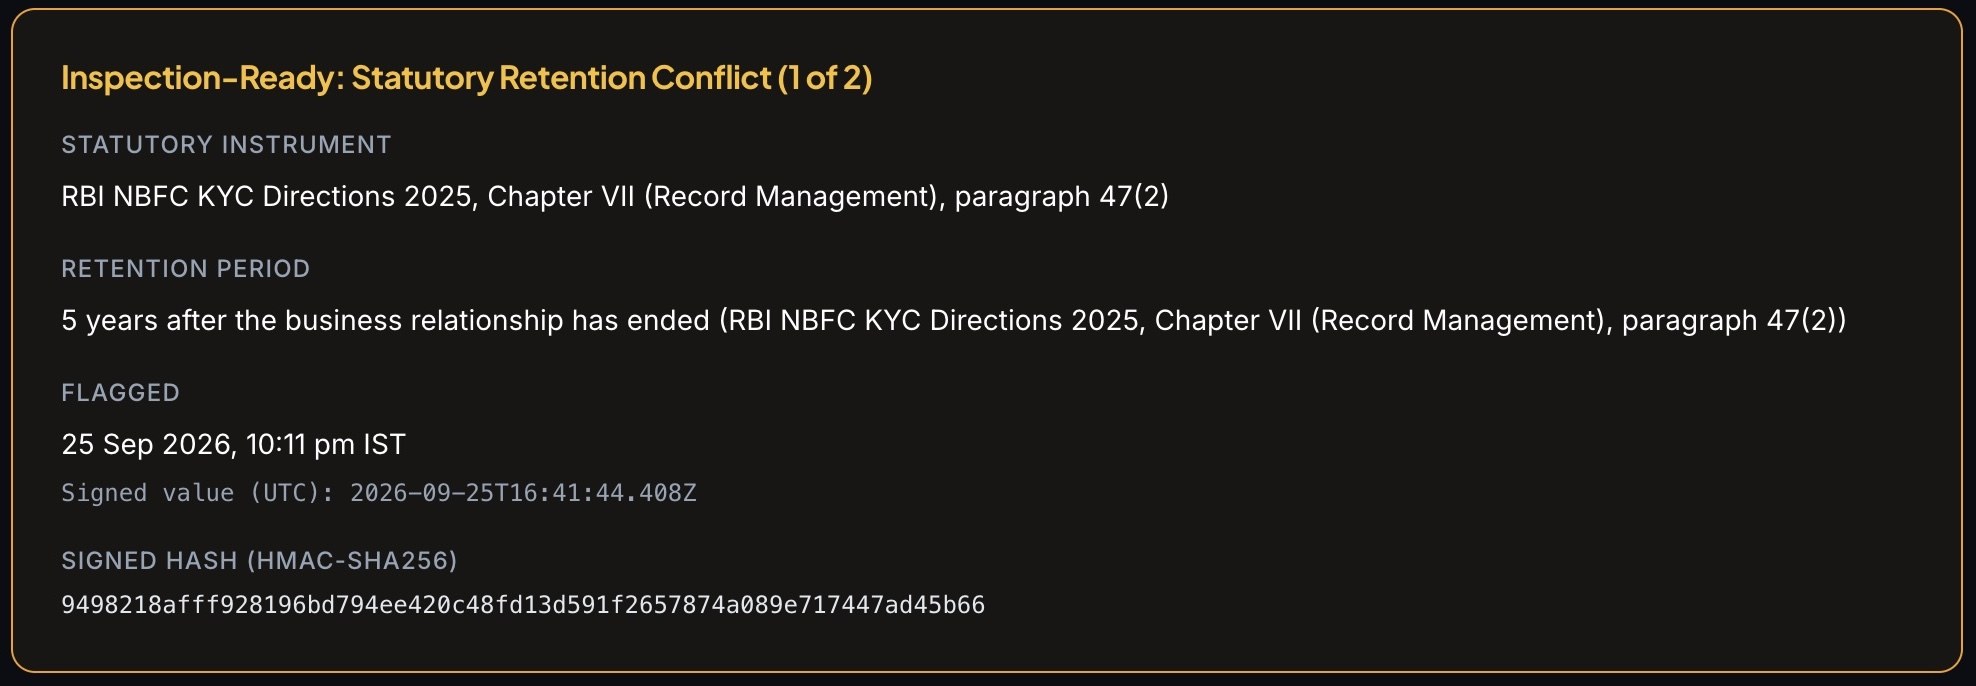
What a denial register entry records
Field names are the columns of the denial register table in the ConsentOS app. The entry holds no name, email or phone number.
dsr_id- The erasure request the entry belongs to.
conflict_id- The conflict register entry that matched, with its regulation, section and DPDP provision.
statutory_instrument- The law that requires the record kept, for example the RBI KYC Directions 2025, Chapter VII (Record Management).
retention_period- How long that law requires it kept, for example five years after the business relationship ends.
event_hash- The HMAC-SHA256 signature over the entry's identifiers, instrument, period and signing time.
created_at_signed- The exact signing timestamp covered by that signature.
What's Included
The Compliance Vault tier.
Built for regulated BFSI entities. Designed around the dual RBI/DPDP compliance requirement. Priced at ₹5,00,000 implementation + ₹1,50,000/month.
Who It's For
Regulated BFSI entities under dual enforcement.
Any entity operating under both RBI regulation and the DPDP Act faces this conflict. The Compliance Vault is the enforcement layer.
NBFCs
Face the full RBI/PMLA/CIBIL/DPDP stack simultaneously. The Legal Obligation Override is designed specifically for the NBFC regulatory profile.
NBFC compliance guide →Fintech Lenders
Digital lenders with RBI NBFC registration or P2P lending licences face the same KYC retention conflict. The Compliance Vault supports resolving it with the same documented override.
Brokers & Insurance
SEBI-registered brokers and IRDAI-regulated insurers carry their own statutory retention obligations. The Compliance Vault's conflict register documents multiple regulatory instruments simultaneously.
Start your Compliance Assessment.
The free assessment takes 10 minutes. You receive a compliance report scored on your answers covering your RBI/DPDP dual obligations, with a prioritised action list.